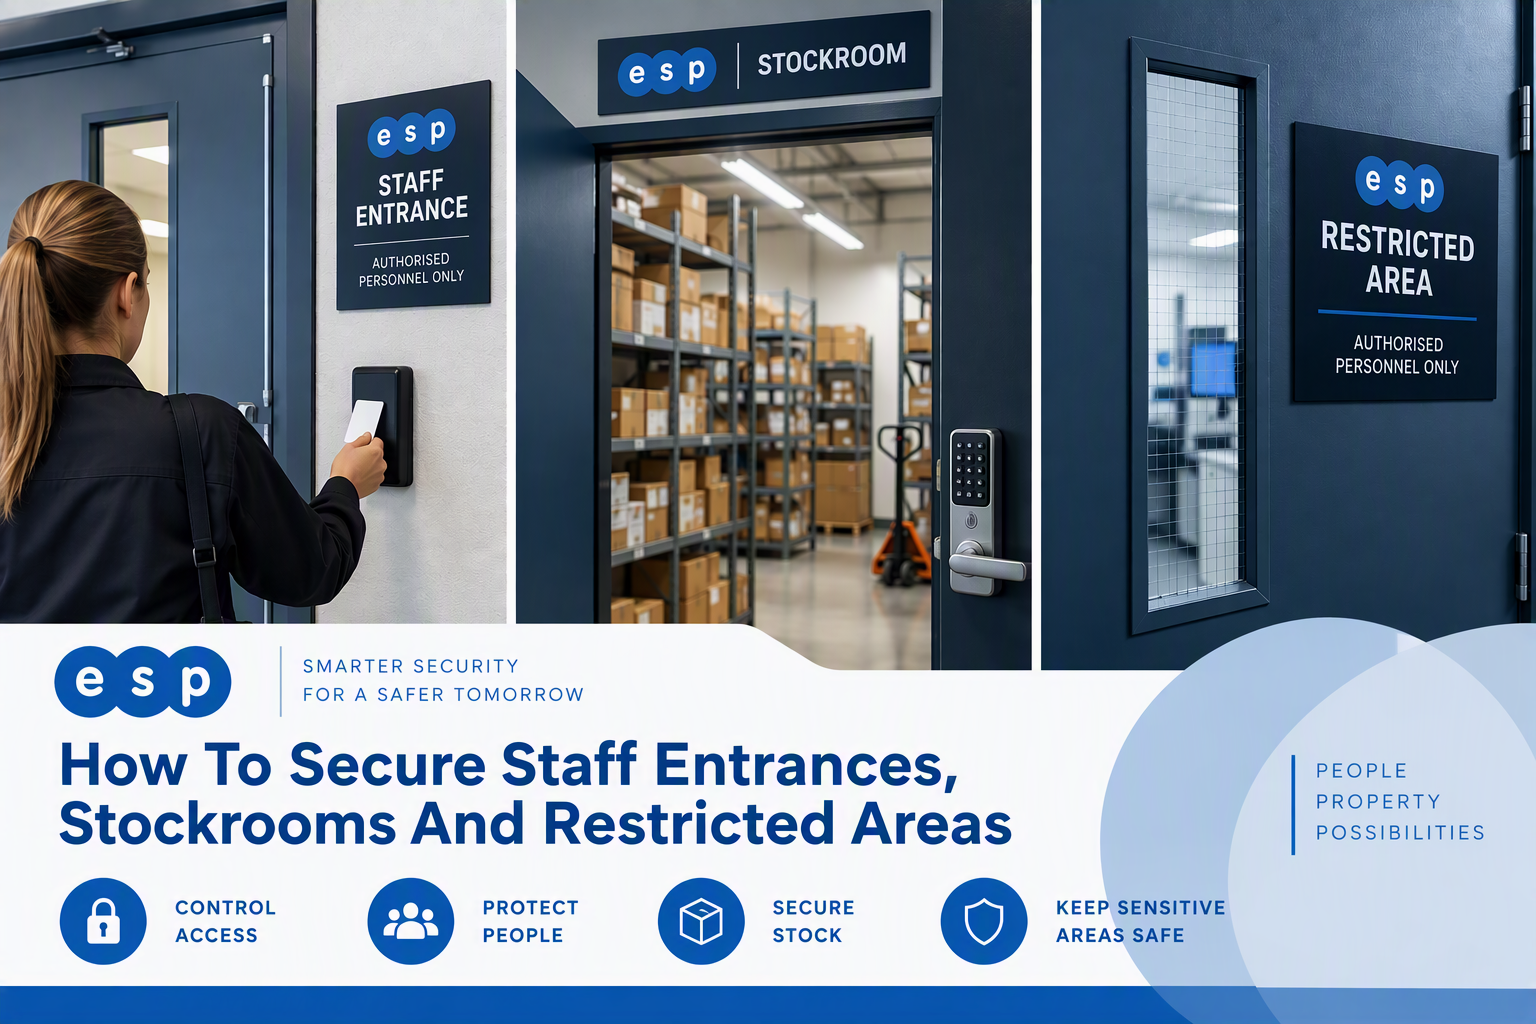
When someone leaves your business or changes job, review their building access at the same time. Disable or amend their door fobs, cards, PINs, access permissions and any relevant administrator logins. Do not rely on collecting a physical fob: cancel its permission in the system as well.
That is the practical answer. Managing access control is not simply a task for the end of an employee’s final day. It involves agreeing who needs each door, deciding when permissions should start or finish, checking temporary credentials and keeping an accurate record of changes.
Electronic Security Protection helps commercial premises plan, install and support physical access control and related CCTV infrastructure.
Why Do Staff Changes Create Security Risks?
Permissions tend to build up as businesses grow. Someone who once worked in a warehouse may now work in an office but still have warehouse access. A former cleaner might still have a working fob. A shared door code may remain unchanged long after several staff members have left.
What Is Permission Creep?
Permission creep means people retain access that is no longer relevant to their current responsibilities. This makes it harder to understand who can enter stockrooms, plant rooms, offices and other restricted spaces.
Why This Matters In Practice
After an incident, an access log may show a valid credential being used, but that does not prove the person should still have permission or that the named holder actually used it. Permission reviews reduce this uncertainty.
Use A Joiner, Mover And Leaver Process
A simple joiner, mover and leaver process makes access changes part of normal business administration rather than something staff remember only when there is a problem. HR or a manager should raise the request, an authorised person should approve it and a designated administrator should make and record the change. This can be delivered by CORE Software which has a Joiners and Leavers module.
New Starters: Give Only the Access Needed
Set permissions according to the person’s role, normal working hours and required locations. A receptionist may need the front entrance and office areas; a warehouse colleague may need goods-in and stockroom doors. Avoid simply copying another employee’s permissions without checking them.
Make Access Dates Clear
Agree when access starts. If a new starter receives credentials in advance, check that it cannot be used earlier than intended.
Role Changes: Remove Old Permissions
When somebody changes department, moves site or takes on new responsibilities, compare their existing access with the new role. Remove unnecessary permissions and add the new ones in a coordinated way, without disrupting legitimate work.
A Common Example
A warehouse supervisor moving into an office-based role may need different entrance hours and no longer require access to loading areas. That change should be documented rather than left until the next security review.
Leavers: Disable Access At The Agreed Time
Set an agreed access cut-off with the relevant manager or HR contact. For a routine departure this may be at the end of the last authorised shift. Higher-risk or unexpected departures may require a different, coordinated approach. Do not automatically disable someone while they still need authorised access to complete their work or leave safely.
What If The Fob Is Not Returned?
Disable the lost or unreturned credential in the system. Retrieving it is useful for stock control, but it is not a substitute for revoking permission. Review mechanical keys separately, because cancelling a fob does not invalidate a physical key.
Cards, Fobs And PINs: What Should Be Checked?
Different entry methods create different risks. The best process depends on whether staff have individual credentials, shared codes or a mixture.
Named Cards And Fobs
Individual credentials are easier to issue, track and disable. Keep the user list up to date, record replacements and promptly disable lost items. Electronic Security Protection’s commercial access control systems include Paxton Net2 solutions for managing access across doors and areas.
What Named Credentials Cannot Prove
A door log records which credential was used, not necessarily which person walked through. Shared cards, tailgating and lending a fob can undermine accountability, so staff procedures matter too.
Shared PINs And Contractor Codes
Shared codes can be convenient but may be known by more people than expected. When someone who knows a shared PIN leaves, assess whether it must be changed and how the new code will be issued securely. For sensitive areas, individual credentials can be easier to manage.
Consider The Disruption
Changing a shared code can mean informing every legitimate user. That administrative cost is a reason to avoid relying on one widely shared PIN for several doors.
How Should Temporary Staff And Contractors Be Managed?
Cleaners, temporary workers, maintenance engineers and contractors may need access for specific dates or hours. Give them only the doors and times necessary for the work, assign a sponsor or manager and define who will end their access.
Use An Expiry Date Where Supported
Time-limited access can reduce forgotten credentials, provided the particular system supports the feature and it is configured correctly. Otherwise, schedule a removal reminder and check it has been completed.
Ask Who Owns The Credential
A contractor’s card should have a clear owner, work purpose and end date. Avoid keeping spare active fobs indefinitely in an unlocked drawer.
Can Access Logs Help After An Incident?
Yes. Access control logs can help establish which credential was presented at which door and at what time. They can support a review of out-of-hours entry or help investigate a missing item, but do not prove a person’s identity on their own. CORE Software can help with this as it makes searching access logs much easier when connected to Paxton Net2.
Use CCTV Only Where It Has A Clear Purpose
Where proportionate, CCTV near staff doors, stockrooms or loading areas can add useful context to access events. Our guide on planning CCTV and access control together explains the distinction between controlling entry and recording activity.
Do Not Assume the Systems Automatically Integrate
Some setups allow linked events, but compatibility and configuration vary. Even without software integration, accurate timestamps and sensible camera positioning can assist a manual review. Plan requirements before promising automatic video matching.
Keep Employee Monitoring Proportionate
Access logs can be personal data. The ICO’s guidance on monitoring workers includes access control and explains why employers should be transparent, assess necessity and protect information collected about workers. Set appropriate access restrictions and retention periods rather than keeping logs indefinitely without justification.
Who Should View Logs?
Limit access to authorised people with a genuine business need. Keep the purpose of log reviews clear and avoid using security data for unrelated staff monitoring without proper assessment.
What Does Access Control Cost To Manage?
There is no reliable flat cost for every business. An existing electronic system may allow routine user changes through its management software, while a site using shared codes or traditional keys may require more work after each departure. Costs also vary with door count, licences or support arrangements, administrator time and whether equipment needs upgrading.
When Is An Upgrade Worth Considering?
If you cannot identify active credentials, struggle to remove former staff promptly or cannot manage different sites consistently, a review may be worthwhile. It does not automatically mean replacing every reader or lock.
Questions To Ask Before Spending
Ask whether existing equipment can be retained, whether permissions can be grouped by role, how lost credentials are cancelled, what training administrators need and what ongoing support is included. Compare the full operational cost, not just installation price.
What About CCTV Apps And Digital Accounts?
Physical access is the focus here, but somebody leaving may also have administrator access to door software, mobile security apps or CCTV viewing. Include these accounts in the wider IT leaver process. The NCSC’s device-security guidance covers practical steps such as changing default passwords and keeping software updated.
Agree Responsibilities Between Teams
HR should confirm the change and effective date, managers should authorise needed areas, facilities or security should update doors, and IT should handle relevant digital accounts. One shared checklist helps prevent gaps.
Do Not Assume Disabling A Fob Disables An App
Physical and digital permissions may sit in different systems. Check each separately, including shared administrator accounts if the person knew the password.
Staff Access Control Checklist
- Confirm the leaving or role-change date and authorised cut-off time
- List doors, sites and restricted areas currently assigned
- Remove unnecessary permissions or disable the person’s credentials
- Collect cards, fobs and physical keys where possible
- Review shared PINs, contractor access and spare credentials
- Check any relevant CCTV or access-control software accounts
- Record who approved and completed each change
- Test that access works or is blocked as intended
- Review active users regularly as the organisation changes
Discuss Staff Access Control With Electronic Security Protection
Keeping door permissions current is often a process improvement, not a major equipment replacement. If your site has former employees still listed, shared codes that have not changed or several buildings with different procedures, an access review can help identify priorities.
Call 0330 2020 101 or contact Electronic Security Protection to discuss access control at your premises and request a quotation.